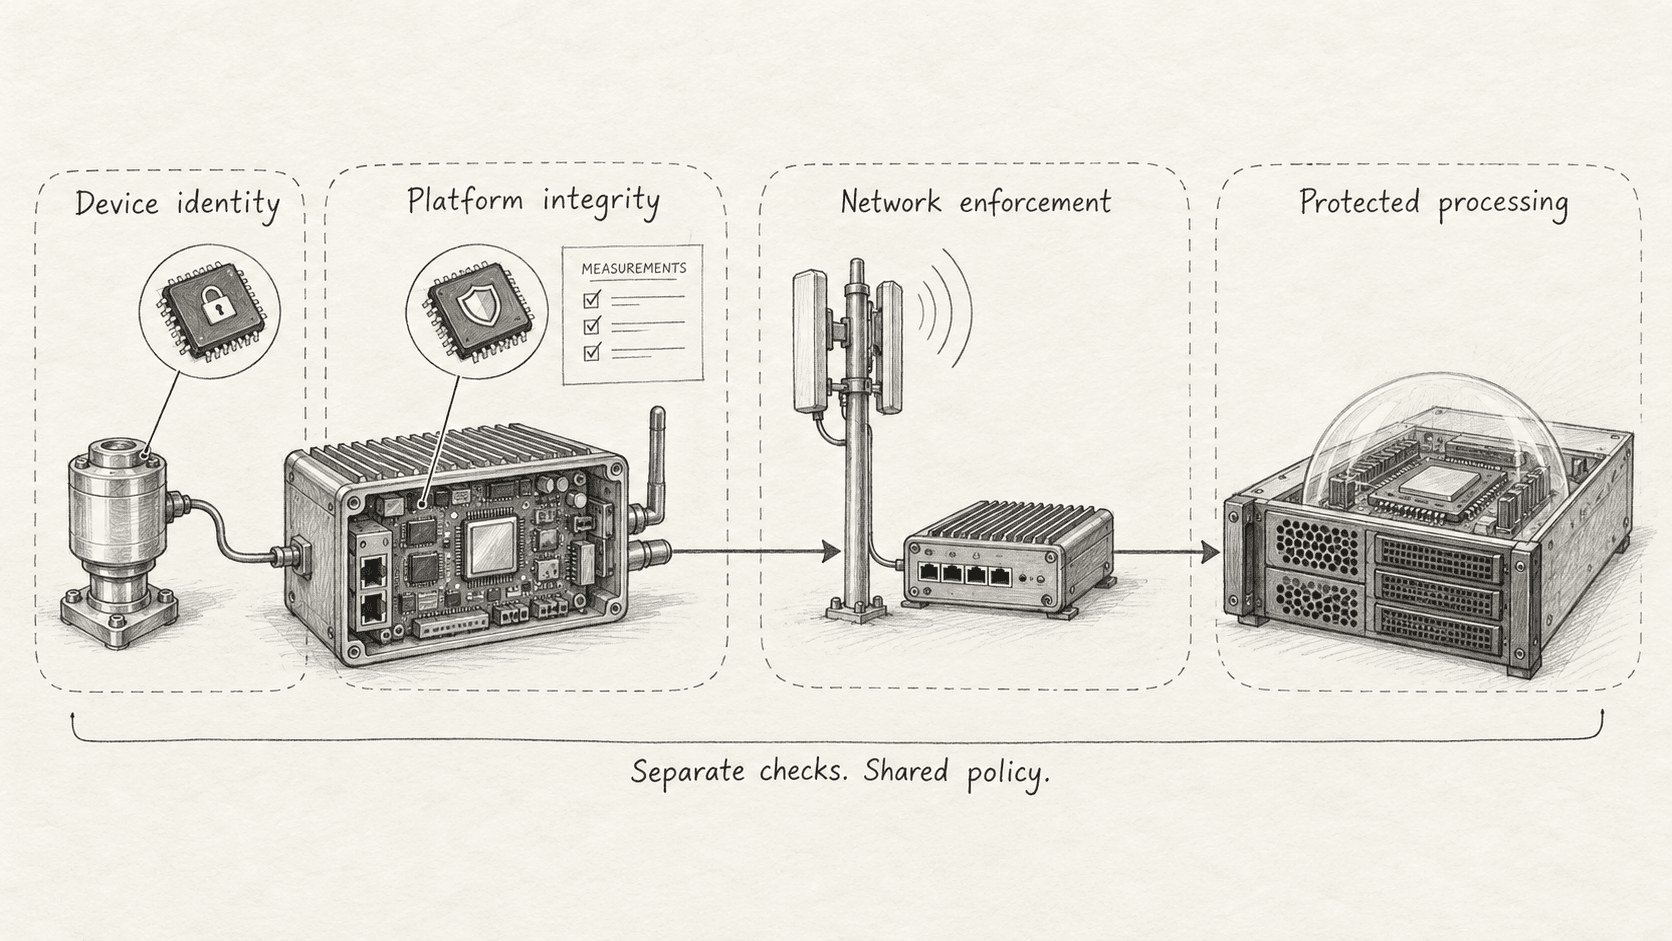
Private 5G IoT security needs more than a successful network connection. A device can hold a valid subscription while its software is outdated, its application permissions are too broad, or the server processing its data is outside an approved trust boundary.
For a team running industrial sensors, gateways or edge analytics, these are separate decisions with different owners. Treating them as one authentication check leaves gaps that are difficult to see until a device changes state or an operational dependency fails.
Our proposed reference model separates four boundaries: device identity, platform integrity, network behavior and sensitive processing. This guide explains what each boundary should check and how to connect their decisions without making every packet wait for a remote service.